Social Events & Meetings
Time for Staff Awareness Sessions by Sponsor Alchemy
Time for Staff Awareness Sessions by Sponsor Alchemy
A recent report by the Institute of Directors (IoD) based on a survey by the IoD and Barclays Bank reported that whilst 95% of respondents considered cyber security to be important to their business 45% still lacked a formal cyber security strategy. Some 40% of respondents would not know who to contact if they were the victim of an attack.
The report says: "Over the last 12 months, the number of cyber security incidents has continued to increase, and more and more it is being demonstrated that it isn’t just ‘the usual suspects’ being attacked. From Lincolnshire County Council to Tesco Bank, it’s clear that cyber security is an issue for just about every organisation. With new legislation in the form of the EU’s GDPR on the way, firms must ensure that they’re equipped for the 21st century."
Only 44% of respondents had provided their staff with cyber awareness training and many left gaps of more than a year between their training programmes. Since staff are invariably the weakest links in cyber security this is a particularly worrying statistic. Firms need to develop and deliver robust staff awareness programmes.
Is it really that urgent?
As cyber crime increases and with GDPR on the horizon the time for action is NOW – no more hoping that it won’t happen to your firm; no more hiding under a blanket of false security. Law and accounting firms as well as organisations in the health sector are particularly vulnerable given the vast amounts of client data that they hold. Phishing and social engineering attacks are growing exponentially.
Marc Dautlich, Data Legislation Partner at Pinsent Masons LLP warns in the IoD report: “Today, many personal data breaches in the UK go unreported by businesses. In jurisdictions that already have mandatory breach reporting requirements, such as the US, unprepared directors have found themselves losing their job after a breach for failing to give adequate attention to the issue, and therefore letting down their stakeholders, damaging their business’s reputation, and exposing it to regulatory and legal sanctions. The mandatory requirement to report security breaches will bring an increased risk of quasi
‘class action’ lawsuits in the UK. Furthermore, negative publicity tends to drive regulators to use their powers in a more robust way: under GeneralData Protection Regulation they will have power to award substantial fines to UK businesses.”
How can YOUR firm be more cyber resilient?
These are some of the steps you should be taking:
- Conduct a full security audit
- Get Cyber Essentials or Cyber Essentials Plus certification
- Develop a cyber security strategy
- Have cyber security policies
- Develop and deliver a staff awareness programme
- Regularly update staff on security issues
- Use vulnerability and penetration testing
What should be covered in staff awareness training?
A good cyber awareness programme should cover – as a minimum – all of the following:
- Threats to your business
- How a cyber attack works
- Types of cyber attack
- Cyber enabled vs Cyber dependent
- Your firms’ cyber policies
- Staying safe
- Updating software
- Scanning computers
- Passwords
- Emails
- Social media platforms
- Working off-site
- BYODs
- What to do if you’re attacked or notice something suspicious
Does your firm have a cyber security strategy?
Does your firm provide cyber awareness training?
Alchemy Systems have 20 years of IT systems experience and are a Microsoft Partner. Alchemy Systems Designs, Supplies, Installs, Supports and Protects clients’ IT systems. The legal sector has always been a strategic focus. Our staff are experienced in the specific needs and challenges of law firms from service desk to strategy to protection services.
Tel. 0330-043-0801
email.info@alchemysys.co.uk
Like Back to Top Seen 511 times Liked 0 times
Subscribe to Updates
If you enjoyed this, why not subscribe to free email updates and join over 1297 subscribers today!
Subscribe to Events updates
Alternatively, you can subscribe via RSS 
All email subscriptions must be confirmed to comply with GDPR.
Related Posts
05th September 2017 | May 2017

LawCare - Mental Health: Are we Thriving or Surviving? Mental Health: Are We Thriving or Surviving? We all have mental health, just as we have physical health. Mental healthincludes our emotional, psychological, and social well-being, and affects how we think, feel, and act. It also helps determine how we handle stress, relate to others, and make choices. Mental healthissues range from the worries we all experience as part of everyday life, to serious long-term conditions. It can be easy to dismiss mental health problems as something that happen to other people, but research shows that 1 in 4 of us will experience them each year. And the legal community is no exception. Many legal professionals are reluctant to talk openly about mental health in the workplace, for fear they may be perceived as weak or not coping with the demands of their role. At LawCare we know that talking is an important first step in changing the way we think and act about mental health. We want to get the legal community talking about mental health so that anyone who has a problem can get support. The theme for Mental Health Awareness Week, which runs from May 8 -14, is Surviving or Thriving? and this year, rather than asking why so many people are living with mental health problems, the aim is to uncover why too few of us are thriving with good mental health. Good mental health is more than the absence of a mental health problem: people are struggling to cope with the demands of life, and are stuck on getting through the day. In terms of thriving, resilience is now recognised as an important factor in the workplace. In the increasingly demanding and changing legal environment, resilience is important in order to thrive. Resilience is defined as the ability to resist or bounce back from adversity, and in any workplace there will be people who thrive on challenges and difficulties, while others will find it hard to cope with unexpected change or problems. If someone finds it hard to forge ahead when things go wrong, the good news is that we can all learn how to develop resilience, and it’s not that difficult. Highly resilient people are flexible, adapt to new circumstances quickly, and thrive in times of constant change. Most importantly, they expect to bounce back, and feel confident that they will. That expectation is closely linked to a general sense of optimism, and finding the positive aspects in most situations is a skill that can be evolved: the right mental attitude to cope, and even flourish, when the going gets tough, can be developed. Ten tips to build resilience: Learn to see challenges, mistakes and failures as valuable learning experiences Give ourselves a pat on the back when things go well. Be kind and forgive ourselves when things go wrong Don’t give in to negative thoughts. Challenge them, and ask whether they are true or realistic Use humour to defuse and downplay difficulties. We can laugh at ourselves and situations Be flexible. Recognise that nothing stays the same, especially in the workplace Take care of physical and mental health. Get enough sleep, exercise and eat well. When our physical self is in good shape, we are less fragile Take time off work, use holiday entitlements and take breaks during the working day Recognise that a bad situation is usually temporary Build a support network. Make time for friends and family who offer encouragement and strength. Consult supportive work colleagues Don’t extrapolate one bad situation into another unrelated situation. We can’t be good at everything, recognise areas of strength Attitude and perspective are fundamental to building resilience: paying attention to strengths and how to develop them, learning to accept that things won’t always go well, focusing on what is working rather than what’s not, and we will all be on our way to thriving, rather than just surviving. We need to com...
05th September 2017 | May 2017

News from the Devon & Somerset Junior Lawyers' Division This month's article has been written by the JLD's Charity Representative, Jessica Tallon. As Charity Representative of the Devon and Somerset JLD, I actively encourage JLD members to raise money for the JLD charity of the year through organised charity events and JLD social events. In November 2016, the Devon and Somerset JLD committee voted for YMCA Exeter to be their charity of the year for 2017. YMCA Exeter supports young people in Exeter through a wide range of Youth Services including homelessness support, youth clubs and a mentoring scheme for ex-offenders. To get our fundraising efforts off to a good start, 7 JLD members set themselves the challenge of participating in the YMCA Sleep Easy 2017 event which involved spending a night sleeping rough in the grounds of Exeter Castle on 4 March 2017. Despite the terrible weather conditions with strong winds and rain throughout the night, our participating JLD members spent the night sleeping on the cobbles with nothing but a sleeping bag and a cardboard box. The JLD set themselves a fundraising target of £500. I am pleased to report that the Devon and Somerset JLD raised an incredible £830 for YMCA Exeter, smashing their initial fundraising target of £500. Upcoming charity events On 9 May 2017, the Devon and Somerset JLD will be hosting a wine, cheese and charity quiz night to help raise money for YMCA Exeter. Additionally, the Devon and Somerset JLD will be hosting a vintage Hollywood themed summer ball on 9 June 2017 at Sandy Park. This will be a fantastic event including a three course meal, charity raffle, photobooth, jazz band and DJ. Details of the above events will be emailed to all Devon and Somerset JLD members shortly. If you require any further information or would like to get involved in any of our fundraising events, please do not hesitate to contact us at dsjld17@gmail.com....
05th September 2017 | May 2017
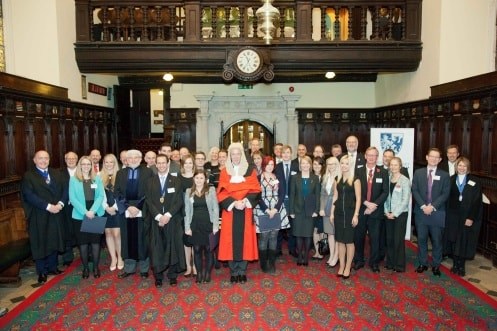
Admissions Ceremony 2017 Invitation DASLS Newly Qualified Solicitors Admissions Ceremony Monday 9th October 2017 at 5.30pm for 6pm at Exeter Guildhall — by invitation only! Did you / will you qualify between 1st September 2016 and 30th September 2017? If so, please contact Monique Bertoni at DASLS office to make sure that you receive your personal invitation. Email: Monique@dasls.com or call 01392 366333 Devon & Somerset Law Society would like to congratulate all NQ Solicitors from Member Firms in DASLS area. Below photo of the 2016 Admissions Ceremony ...
06th March 2020 | March 2020

Dear All, This year really is flying by. I have just had my birthday. After updating you previously on the excellent catch up I had with the Law Society CEO Paul Tennant on his visit to the south west last November, I had not expected to be back in touch with him quite so soon. Sadly, this time it was in less happy circumstances. I was, like many of you, shocked and saddened in January to hear the news and see the pictures of the substantial fire at Chancery Lane in London. I have emailed Paul Tennant and James Shepherd, our Law Society Relationship Management Executive, to send our best wishes and we are hoping that the building will be back to full use very soon. As I write this report, preparations are in full swing for the 2020 DASLS Legal Awards & Dinner. As you know the Annual Dinner is being held again this year at Exeter Cathedral. The event is to take place on the 30th April 2020. After the success of last year, we are hoping that once again the event is sold out which would mean we will have around 480 people attending. If you have not done so already, please contact Llew Nicholls and the team at our Awards partners ‘Grow Marketing’ who have worked very hard alongside our very own Tony and Monique to achieve full sponsorship of this event. You can contact Llew to book the remaining places by emailing Llew directly at Llew@growmarketinguk.com. There have been more nominations than ever before with more entries making the short list. Please do not miss this dazzling occasion. You will all have received DASLS latest 2020 training courses programme. Tony Steiner and the team have worked hard to arrange these events. You will see that as members you get preferential rates and if appropriate reduced rates for multiple attendees from your firms. Please take advantage of these services as a proportion of the monies do go to support our Society’s broad continuing education offering. If I do not see you individually before I look forward to catching up with you at the 2020 DASLS Legal Awards and Annual Dinner in April. With very best wishes Nigel Lyons President 2019-2020...
06th March 2020 | March 2020

New AML Regulations and the pursuit of the beneficial owner. Introduction The new Money Laundering & Terrorist Finance (Amendment) Regulations 2019 which came into force on 10 January have modified a number of aspects of the 2017 AML Regulations, with which we have been complying for some time. However, many firms’ procedures hark back to the earlier days of the 2007 Regulations and have not been modified or updated much over recent years. This article seeks to set out what the new Regulations in fact require, and the steps we should be taking in relevant cases. The Policy It has been true for some time that the ultimate aim of all the regulatory rules is transparency – it has always been the case that the use of artificial structures such as trusts, companies, bearer shares, foundations and charities – whilst perfectly legal – have to some extent also benefitted from the extra anonymity they offer to the true owner and recipient of the funds and services we provide. If we offer services to these types of entity, the Regulations require us to go some way to identifying the individuals who are actually benefitting from our services, and this entails uncovering the true ownership of the organisation. Whilst this would be difficult in many instances – Cayman Island companies with bearer shares, for example – we must nevertheless attempt to get some assurances from the creators of the companies, accountants or registrars as to the ownership of the shares, and have some way of being notified of any change in ownership. We also need to be aware of the PEP and Sanctions status of these individuals. Further, for UK companies, the PSC Regulations 2016 impose an exactly similar obligation on the companies themselves to identify their beneficial owners and notify Companies House of any shareholder with 25% or more of the shares or exercising control over management of the business. The Regulations The Regulations provide that we must, as part of our CDD procedures Identify the client – this means coming to know who they are, by name and some other characteristic, e.g. address, date of birth, date of incorporation Verify that identity – by means of reliable and independent data and documentation Identify the beneficial owner (if the client is an entity) – though not necessarily verifying that identity Identify and verify the identity of the person actually instructing us (if not already done). What this means for us When acting for a COMPANY (that is not a listed company) the Regulations require us to obtain Details of the company as registered (which must be proven by a copy of the register entries available from Companies House or equivalent registry) – name, number, registered office address, principal place of business the law to which it is subject details of its governing documentation (its memorandum) names of the directors. Names of any beneficial owners, and the identity of any individual owners of legal entities which own the client Names and verification of the persons instructing us on behalf of the company, and their authority to do so. Note that we cannot rely on the information provided by the company under the PSC Regulations but we must undertake our own research in order to fulfil our CDD duties. Further, if as part of that research, we discover that the Companies House data on PSC’s is incorrect, then we are now under a further obligation to notify the Registrar of Companies of this fact. We also need to establish that PEPs and Sanctions checks are also undertaken. If genuinely positive entries are revealed in response we should undertake enhanced CDD steps or cease to act, accordingly. Electronic searches are a permissible avenue to use provided the search provider can offer us the necessary assurances that the person actually claiming an identity is IN FACT that person. Check also whether ...